
Once an incident is declared, our Incident Response (IR) team activates immediately to guide you through a structured containment and recovery process. We work to minimize business disruption and data loss by providing clear technical direction and strategic advice during a crisis. Our goal is to bring your systems back to a known good state as quickly and safely as possible.

Incident Response
When an incident happens, every minute matters. Our incident response team deploys rapidly to contain threats, preserve evidence, and restore operations.
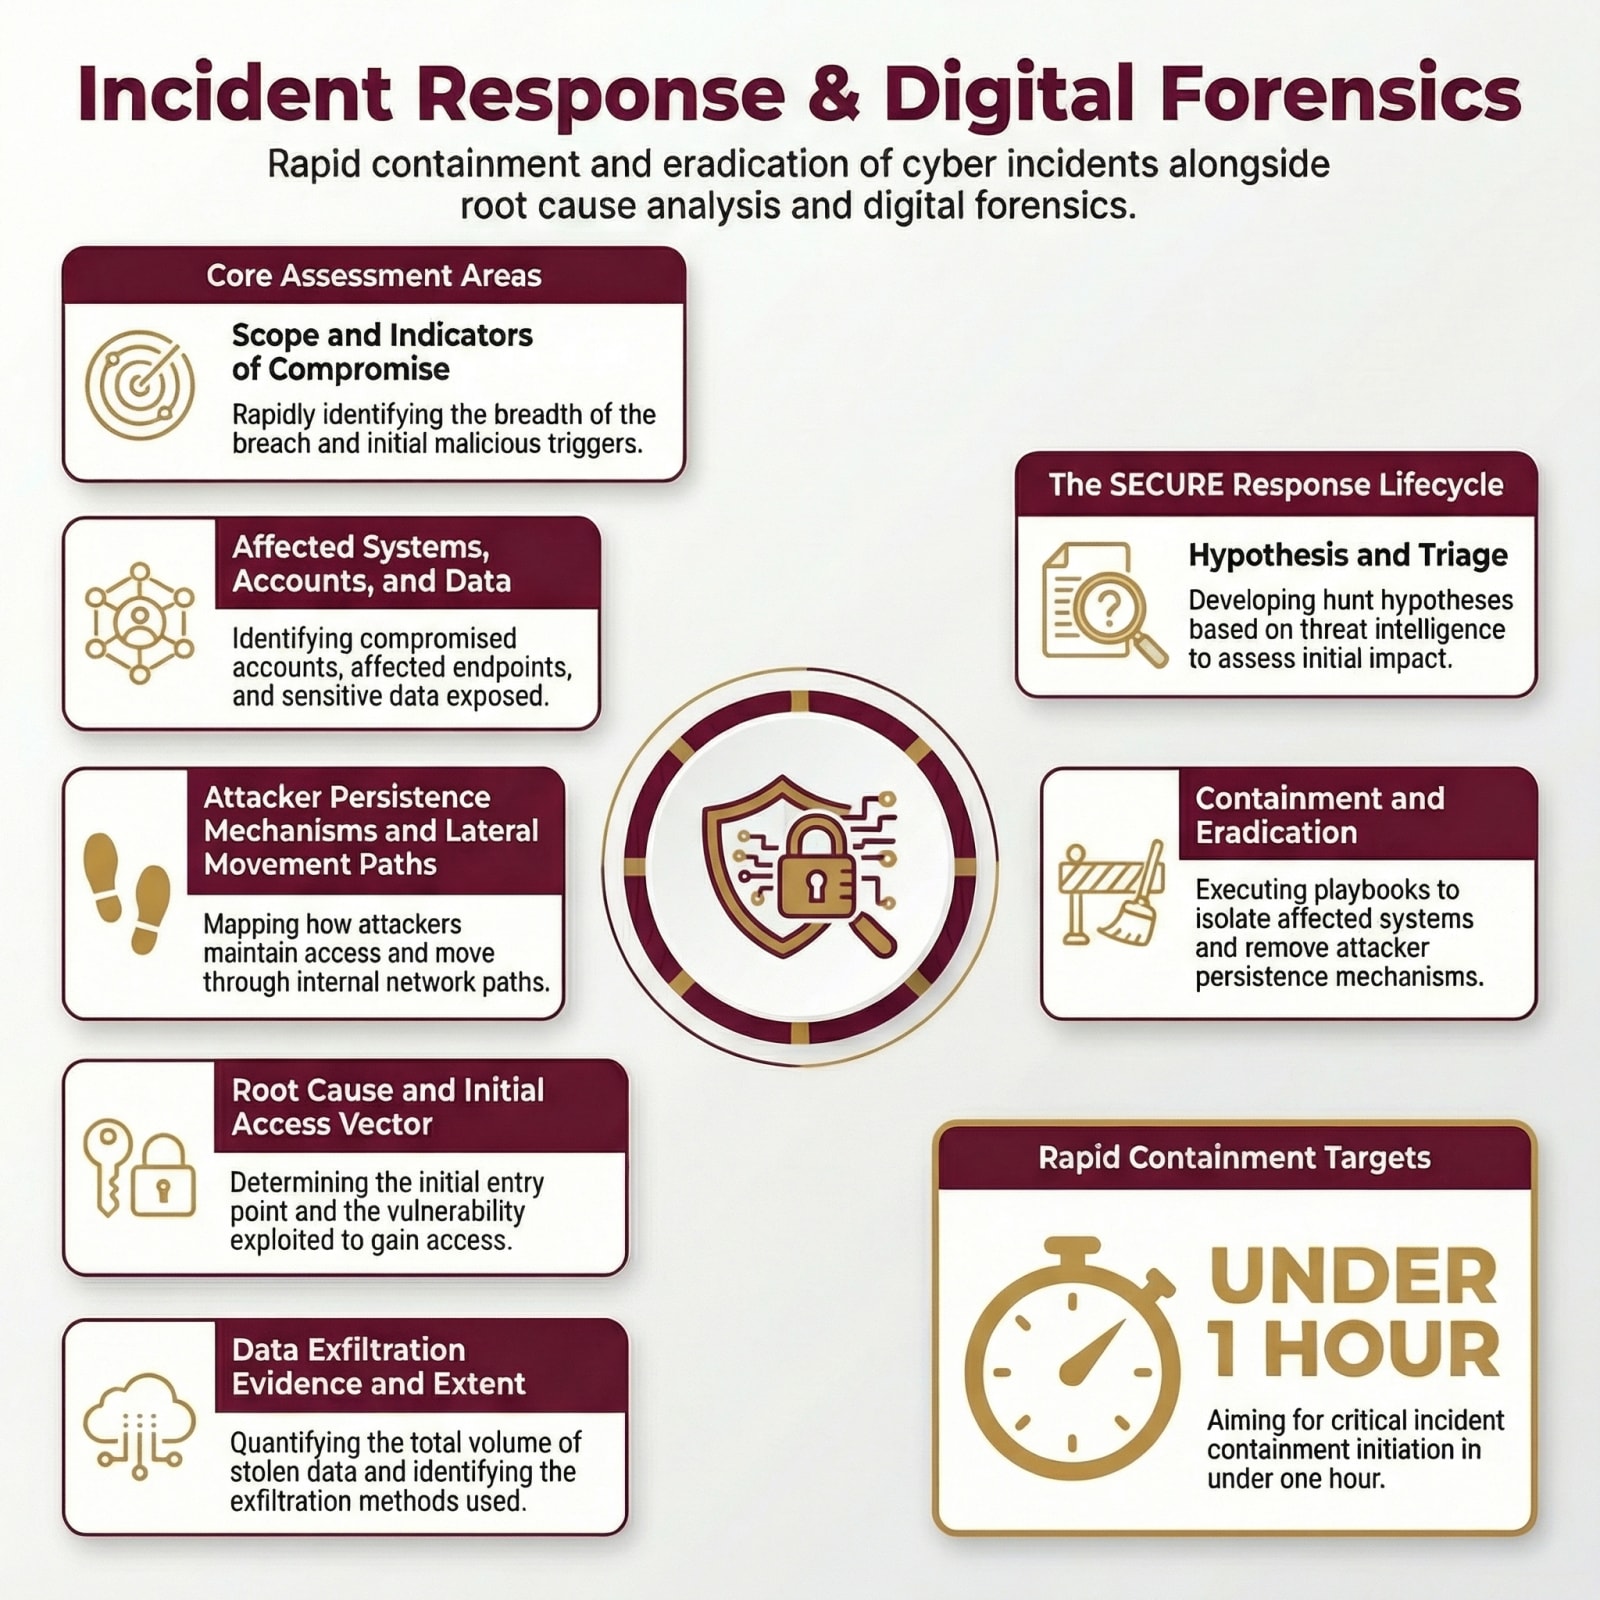
Scope of Assessment
What We Assess
The areas we examine during a Incident Response engagement, and what each one is looking for.
01
Initial Triage & Scope
Define incident scope and analyze early indicators of compromise (IOCs).
02
Impact Assessment
Identify affected systems, compromised user accounts, and leaked data elements.
03
Persistence & Movement
Trace attacker backdoor installations, cronjobs, and lateral network steps.
04
Root Cause Investigation
Pinpoint root vulnerabilities or entry points exploited by attackers.
05
Exfiltration Analysis
Examine traffic logs and file activity for evidence of data exfiltration.
Also in Scope
Containment effectiveness and speed of isolation across affected environments
Post-incident evidence preservation and forensic chain of custody integrity
Remediation completeness and control improvements implemented following closure
Stakeholder communication and regulatory notification workflow execution
Malware analysis and artifact reverse engineering capability during response
Cloud and SaaS environment investigation coverage and tooling adequacy
Lessons learned documentation and post-incident review process maturity
Cyber insurance notification requirements and claim support readiness
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Hypothesis & Triage
Develop hunt hypotheses based on threat intel, or rapidly assess initial incident scope.
02
Investigation
Deploy analysts to investigate network anomalies, telemetry, and forensic data.
03
Containment & Eradication
Isolate affected systems, remove attacker persistence, and recover operations.
04
Post-Incident
Deliver root cause analysis, threat hunt findings, and permanent detection improvements.
Where This Lands
Industry Application

Healthcare & HealthTech
Rapidly containing and recovering from disruptive cyber incidents targeting critical care systems.
Enterprise & Manufacturing
Proactively hunting for dormant adversaries within complex, legacy industrial networks.
Banking & Financial Services
Conducting deep forensic investigations and hunting for sophisticated financial cybercrime.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.
Threat Intelligence & Security Insights Portal
Our Incident Response engagements are accelerated by QPulse, combining platform intelligence with advisory and execution delivery.
- Curated threat intelligence for enterprise context
- Actionable advisories mapped to emerging risks
- Operational insights for proactive defense
Frequently Asked Questions
Answers to common questions for Incident Response.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.