
Yes, our security experts specialize in the unique configurations, services, and security tools native to AWS, Microsoft Azure, and Google Cloud Platform (GCP). Each provider has its own nuances, and we tailor our assessment to leverage the specific security features available on your chosen platform. This specialized knowledge ensures we find vulnerabilities that generic tools might miss.

AWS / Azure / GCP Security Assessment
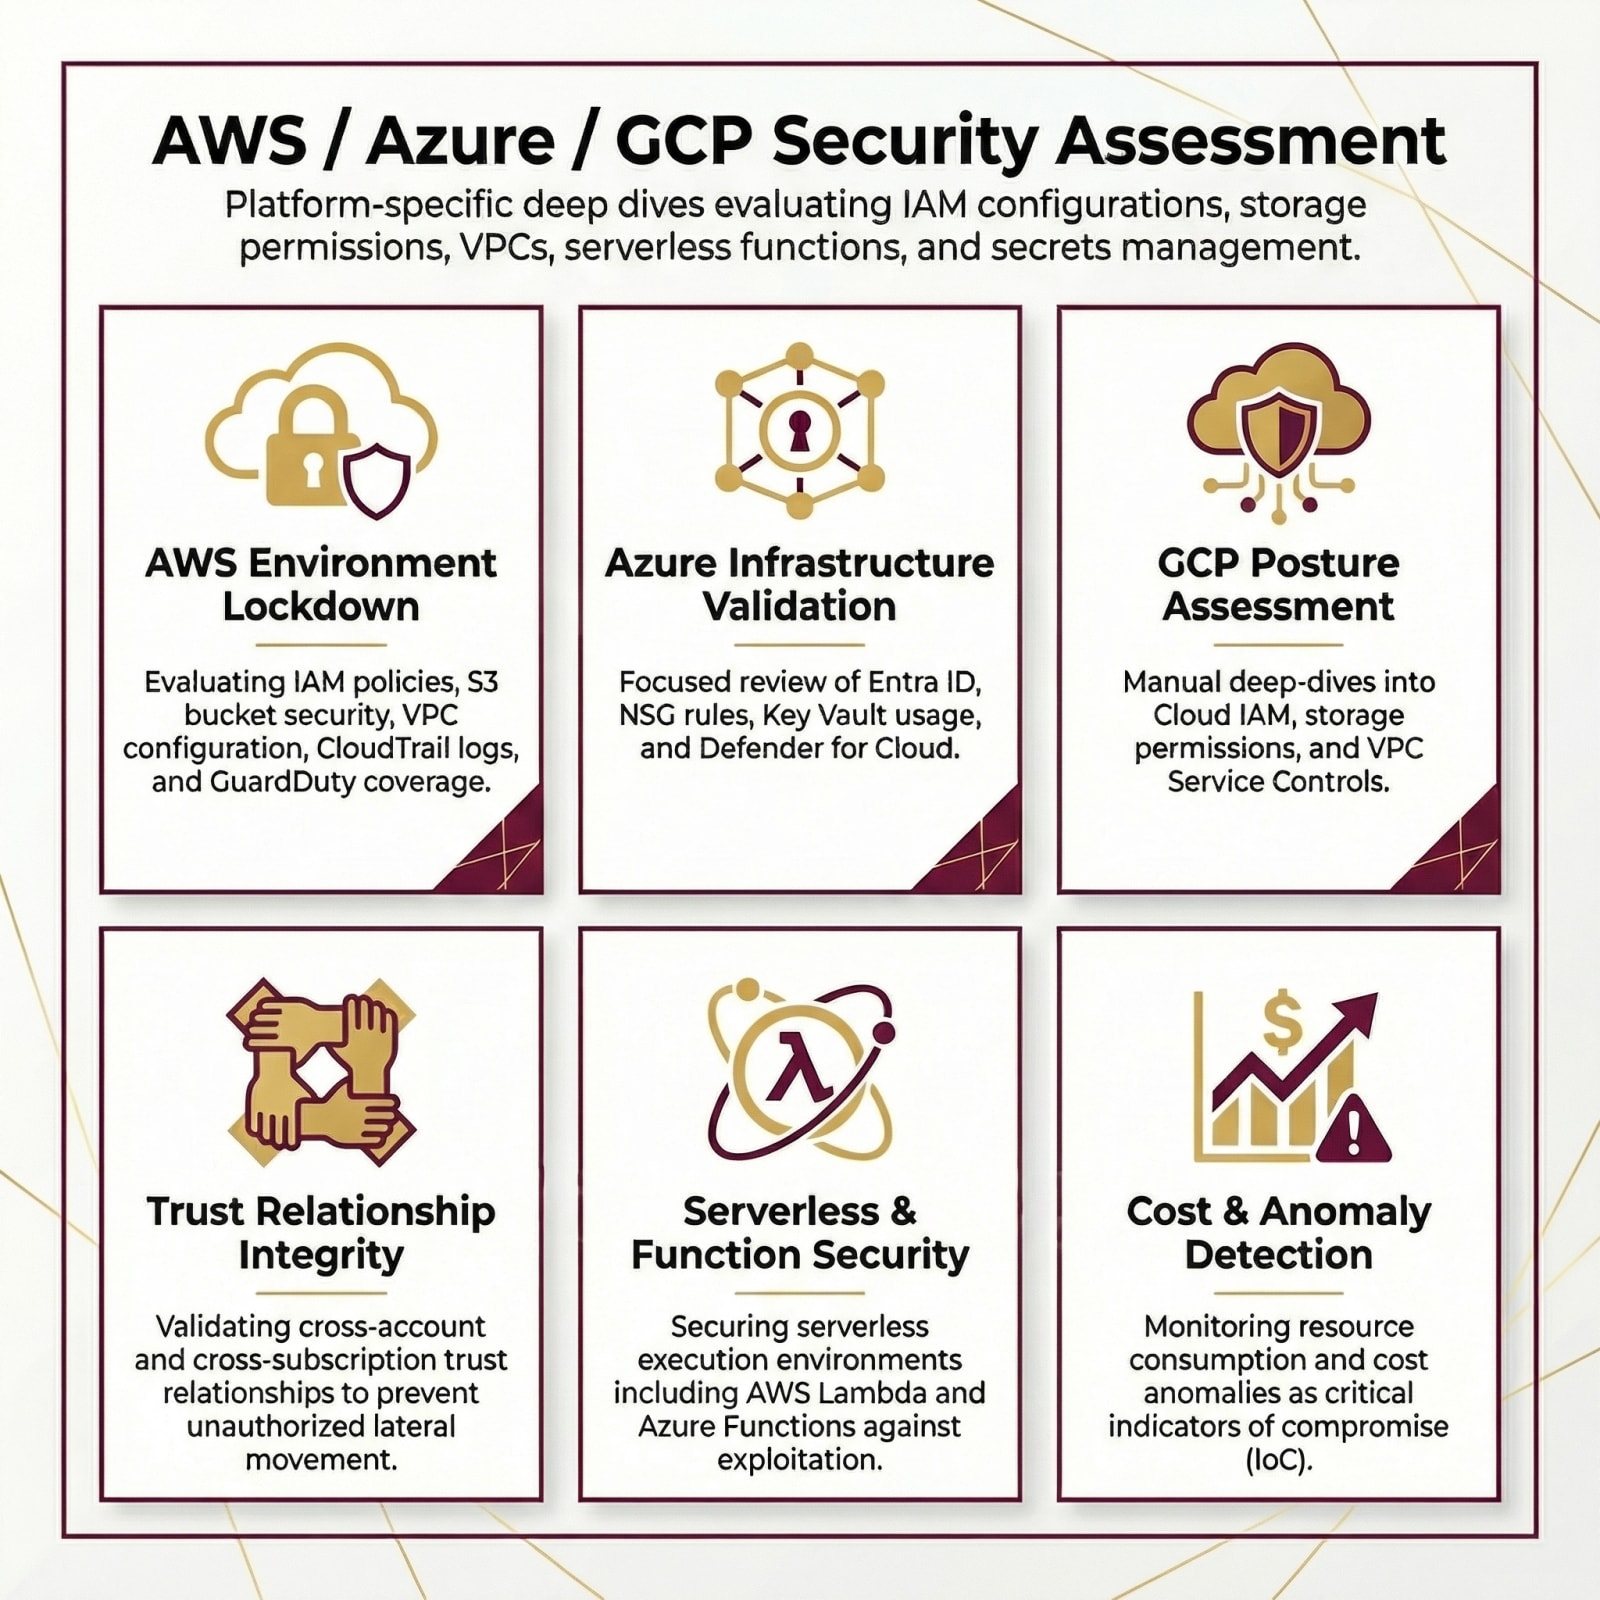
Generic cloud assessments miss platform-specific nuances. Our AWS and Azure specialists assess your environment against platform-native security best practices.
Scope of Assessment
What We Assess
The areas we examine during a AWS / Azure / GCP Security Assessment engagement, and what each one is looking for.
01
AWS Security Audit
Audit AWS IAM, S3 access, VPC config, CloudTrail logs, and GuardDuty alerting.
02
Azure Security Audit
Review Azure Entra ID, Network Security Groups, Key Vault, and Defender alerts.
03
Cross-Account Trust
Assess trust relationships, external roles, and subscription boundaries.
04
Serverless Security
Verify function access controls, environment variables, and execution times.
05
PaaS Security Hardening
Audit managed database, cache, and messaging platform security configurations.
06
Cost Anomaly Detection
Detect resource anomalies or sudden cost spikes indicating server hijack.
Also in Scope
GCP: IAM bindings, VPC service controls, Cloud Armor configuration and Security Command Center coverage
Container and Kubernetes service security across EKS, AKS and GKE environments
Multi-cloud identity federation and cross-platform trust relationship risks
Cloud-native backup, snapshot and recovery configuration security validation
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Discovery
Enumerate all cloud resources, services, and cross-account relationships in scope.
02
Configuration Audit
Run automated assessments against CIS Benchmarks and platform-native standards.
03
Architecture Analysis
Perform manual deep-dives into IAM policies, VPC design, and trust boundaries.
04
Reporting
Deliver risk-rated findings paired with cloud-native remediation scripts and guidance.
Where This Lands
Industry Application
SaaS & Technology
Hardening complex, multi-tenant cloud platforms built on AWS, Azure, or GCP.
FinTech & Digital Payments
Ensuring specialized native services like AWS KMS or Azure Key Vault are implemented securely.
Enterprise & Manufacturing
Securing Azure AD / Entra ID hybrid configurations connecting global plants to the cloud.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
Our AWS / Azure / GCP Security Assessment engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for AWS / Azure / GCP Security Assessment.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.