
Absolutely, because while the cloud is growing rapidly, hybrid environments remain the norm for most large organizations. We provide deep technical hardening for traditional data centers, physical servers, and legacy infrastructure that may not be cloud-ready. Our goal is to ensure that your on-premises defenses are just as robust and modern as your cloud-based ones.

On-Premises & Hybrid Infrastructure Hardening
On-premises infrastructure remains a critical attack surface for most enterprises. We review infrastructure security with adversary-minded assessment methodology.
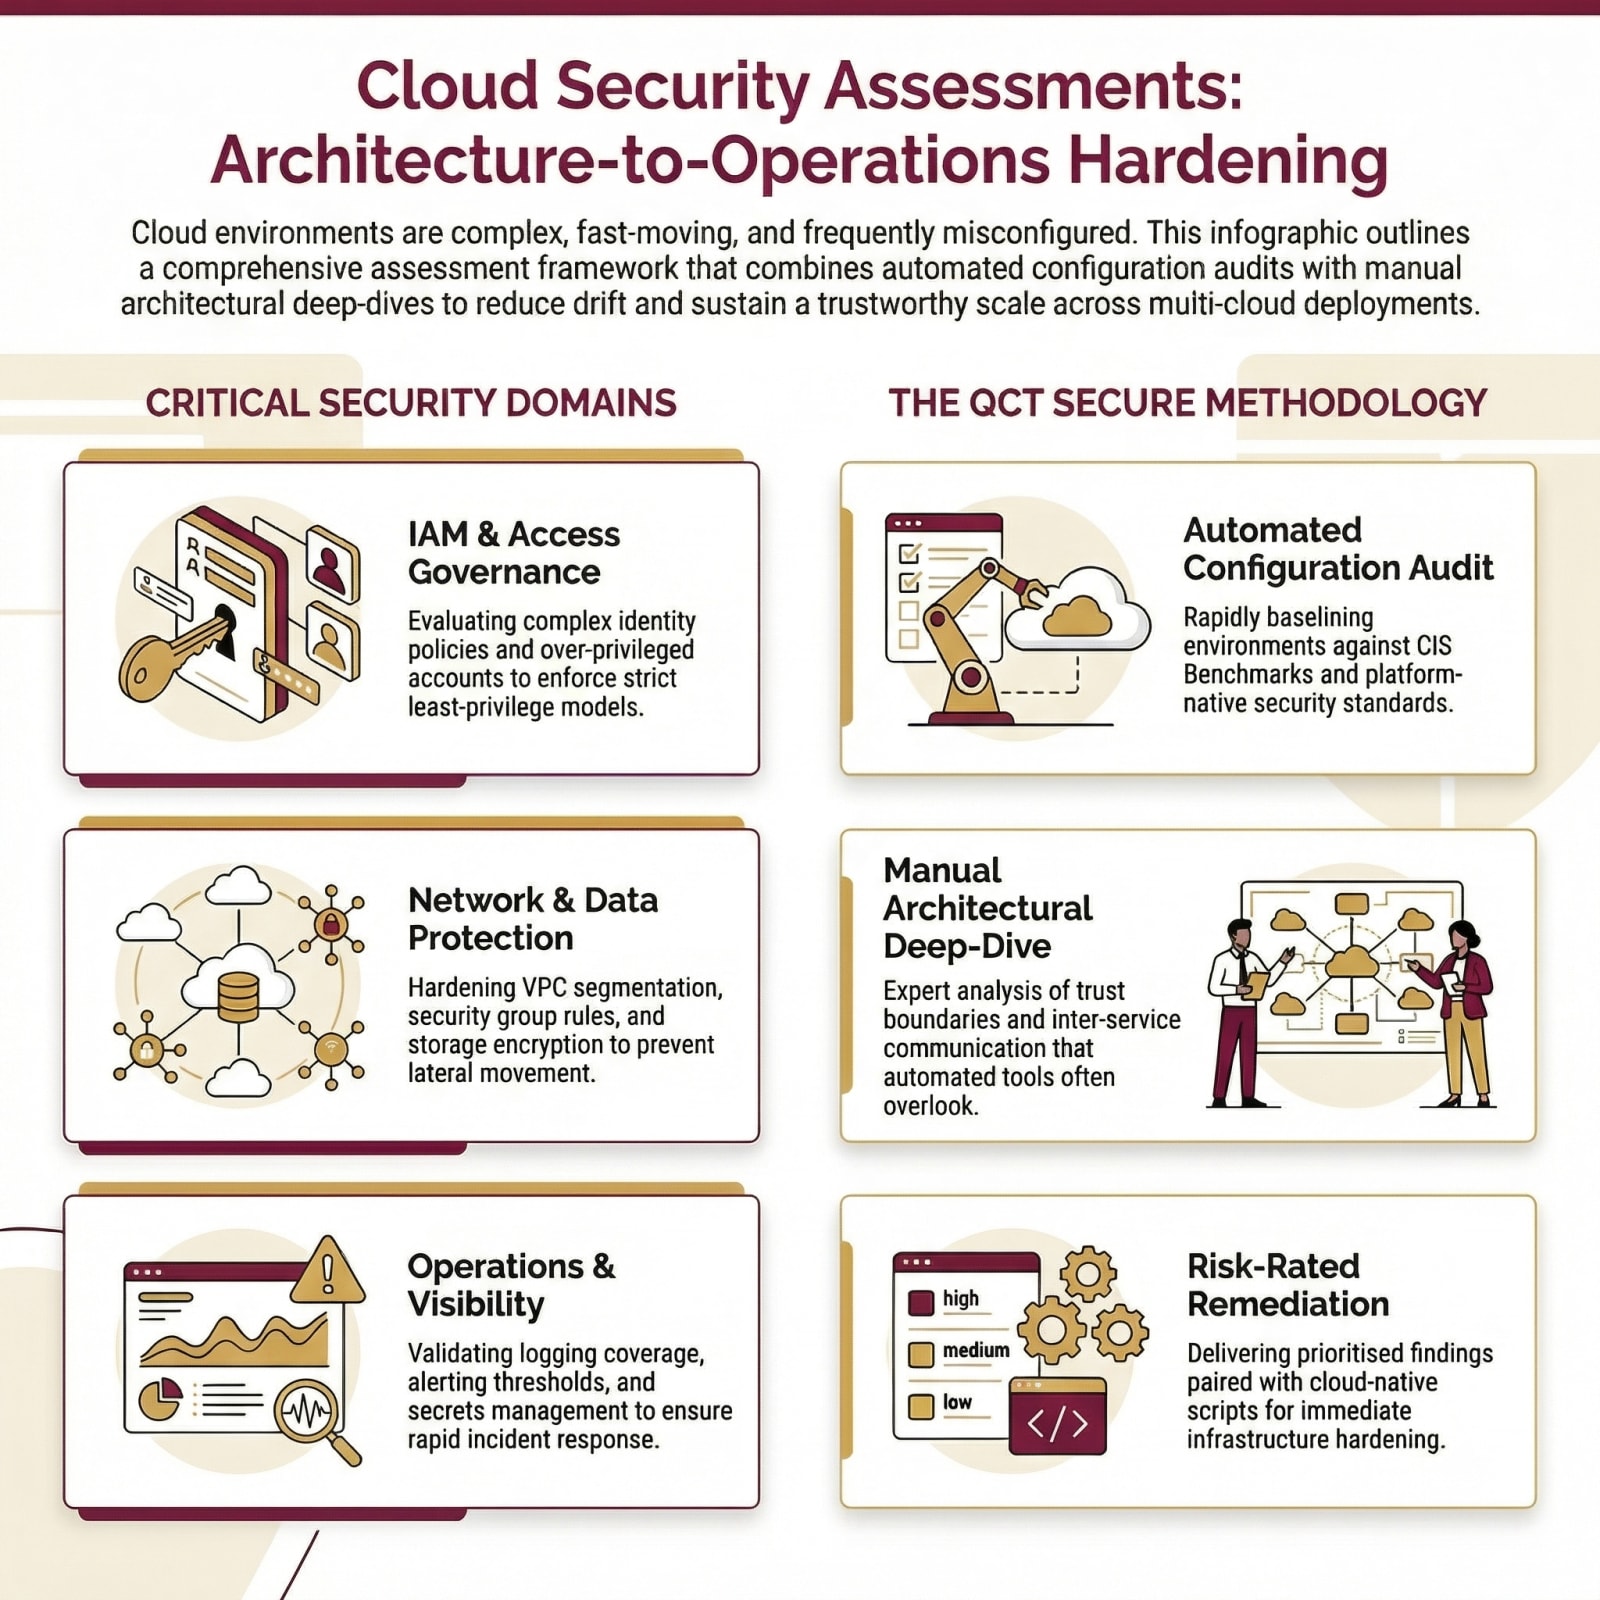
Scope of Assessment
What We Assess
The areas we examine during a On-Premises & Hybrid Infrastructure Hardening engagement, and what each one is looking for.
01
Network Segmentation
Audit internal network routing, VLAN configurations, and routing tables.
02
Firewall Policy Review
Review active firewall rule lists and clean up legacy or open permissions.
03
Server OS Hardening
Check server OS settings against Center for Internet Security (CIS) benchmarks.
04
Active Directory Security
Audit AD domain controllers, trust relationships, group policies, and delegacy.
05
Patch Management
Assess server and workstation patch deployment scope, speed, and automation.
06
Endpoint Security
Verify coverage and policy enforcement of local antivirus and EDR agents.
Also in Scope
Hybrid connectivity security across VPN, Direct Connect and ExpressRoute implementations
Legacy system and end-of-life technology risk within the infrastructure estate
Physical and logical access control integration across on-premises environments
Out-of-band management and administrative network security configuration
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Deployment & Discovery
Implement monitoring tools and inventory all network assets.
02
Baselining
Establish approved security configuration baselines across hybrid environments.
03
Alerting & Analysis
Configure risk-based alerts for configuration drift and assess network segmentation.
04
Reporting
Deliver continuous compliance dashboards and prioritized infrastructure remediation plans.
Where This Lands
Industry Application
Enterprise & Manufacturing
Securing complex, hybrid environments spanning on-premises data centers and the cloud.
Banking & Financial Services
Maintaining rigorous access controls across branch networks and legacy data centers.

Healthcare & HealthTech
Protecting on-premises hospital networks and securing paths to cloud-hosted medical records.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
Our On-Premises & Hybrid Infrastructure Hardening engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for On-Premises & Hybrid Infrastructure Hardening.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.