
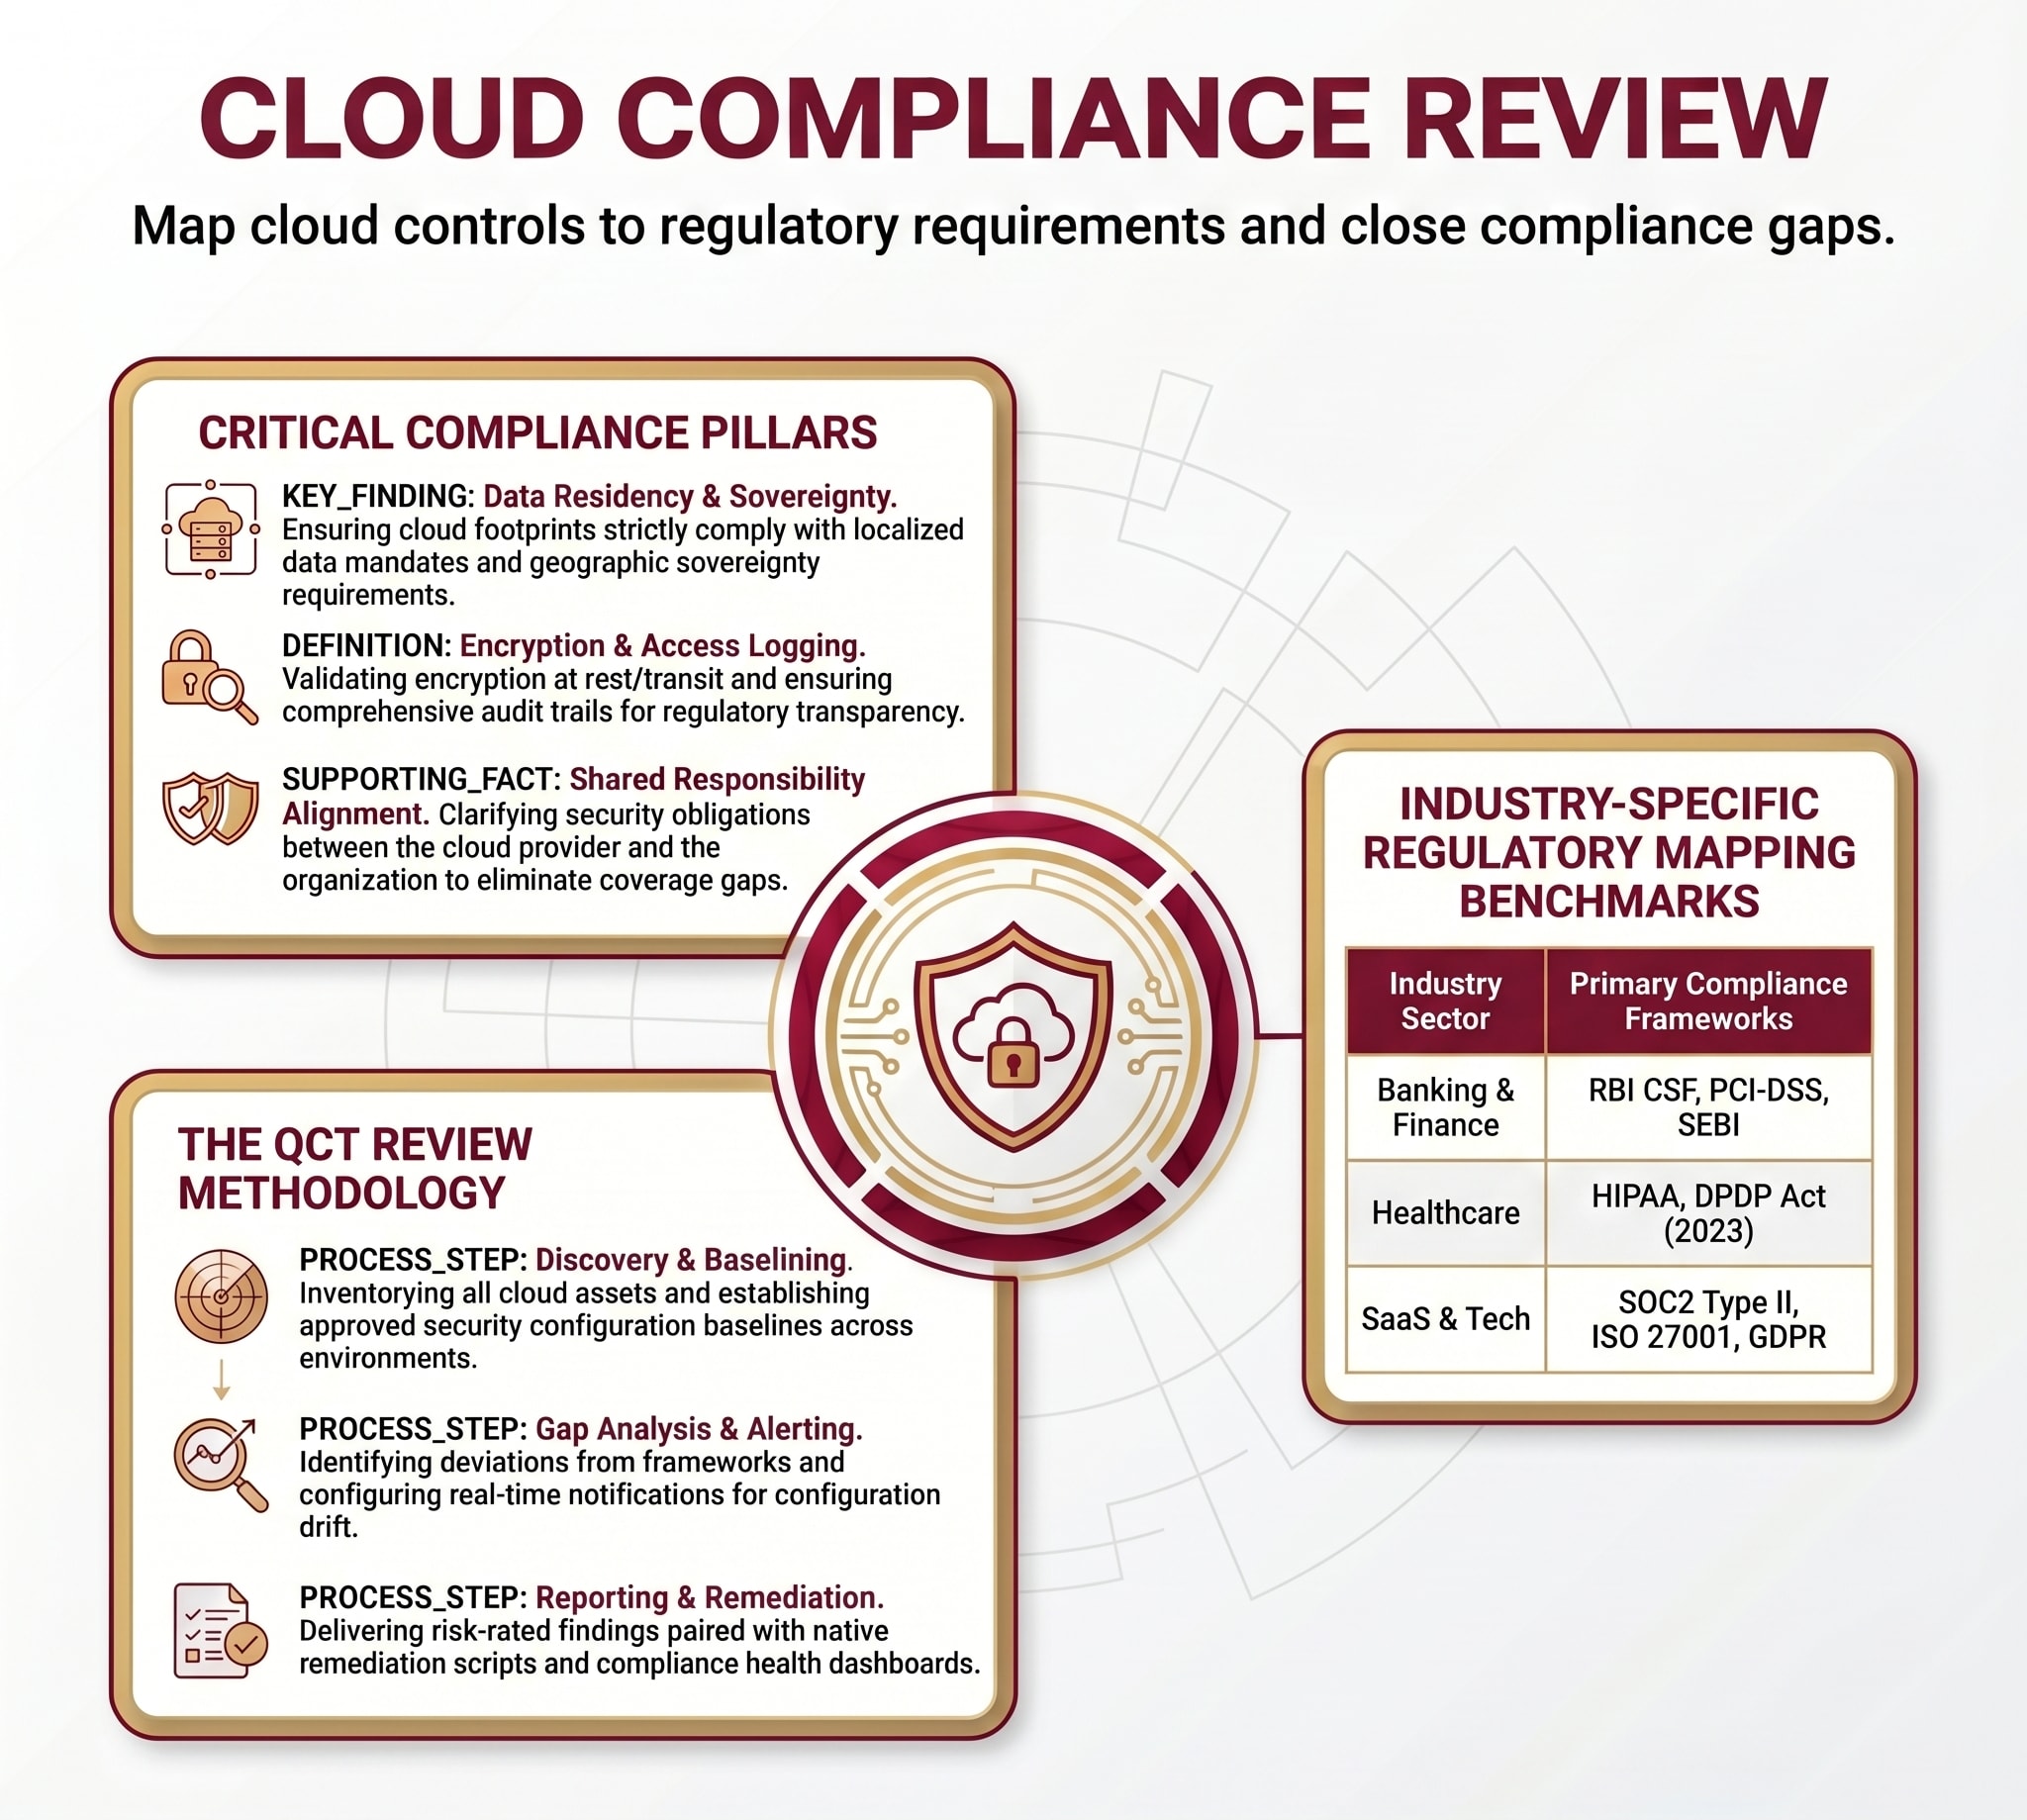
A cloud compliance review ensures that your usage of AWS, Azure, or GCP adheres strictly to industry regulations and legal mandates. We translate complex legal and regulatory text into specific, technical cloud configurations and controls that your team can implement. This process bridges the gap between the legal requirements of your business and the technical reality of your cloud environment.

Cloud Compliance Review
Regulatory frameworks increasingly mandate specific cloud security controls. We map your cloud environment to applicable compliance requirements and identify gaps.
Scope of Assessment
What We Assess
The areas we examine during a Cloud Compliance Review engagement, and what each one is looking for.
01
Data Sovereignty
Audit data residency policies and verify geographical storage locations.
02
Encryption Compliance
Verify that encryption protocols meet regulatory standards across all layers.
03
Audit Log Integrity
Inspect central access logs for retention, formatting, and completeness.
04
Disaster Recovery
Evaluate backup integrity, retention policies, and restoration test outcomes.
05
Shared Responsibility
Clarify ownership and operational handoffs of cloud security responsibilities.
06
Vendor Attestations
Review security attestations, SOC2 reports, and ISO certificates of providers.
Also in Scope
Cloud service configuration alignment against applicable regulatory control requirements
Third-party and marketplace service compliance obligations within the cloud environment
Identity governance and privileged access compliance across cloud platforms
Incident response and forensic readiness within cloud-hosted environments
Security monitoring and alerting adequacy to meet regulatory detection requirements
Cloud exit strategy and data portability controls supporting regulatory obligations
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Deployment & Discovery
Implement monitoring tools and inventory all network assets.
02
Baselining
Establish approved security configuration baselines across hybrid environments.
03
Alerting & Analysis
Configure risk-based alerts for configuration drift and assess network segmentation.
04
Reporting
Deliver continuous compliance dashboards and prioritized infrastructure remediation plans.
Where This Lands
Industry Application
Banking & Financial Services
Ensuring cloud footprints comply with RBI localized data mandates.
FinTech & Digital Payments
Validating cloud PCI-DSS compliance before formal assessment audits.

Healthcare & HealthTech
Ensuring Electronic Health Records (EHR) hosted in the cloud meet HIPAA security rules.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
Our Cloud Compliance Review engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for Cloud Compliance Review.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.